Firewall configuration is the process of setting rules that decide which network traffic gets through to your devices and which gets blocked. In practice, that means telling your router or firewall software which connections to allow in, which to allow out, and shutting the door on everything else by default. Get it wrong and you either leave gaps attackers can walk through, or you block the tools your business actually needs to run.
This matters more than most small business owners realise. The National Cyber Security Centre (NCSC) says that properly implementing its five basic technical controls, starting with firewalls, would stop around 80% of the common cyber attacks UK organisations face. This guide covers what firewall configuration actually involves, how it connects to the UK’s Cyber Essentials scheme, and a step by step walkthrough for setting one up on both your network and your individual devices.
What Firewall Configuration Actually Means
A firewall isn’t a single product, it’s a role that can be filled by different kinds of device or software. Every firewall, whatever form it takes, works by applying rules to traffic based on things like source and destination IP address, port number, and protocol.
Configuration is where the value comes from. A firewall left on its default, out-of-the-box settings offers far less protection than one that’s been reviewed and tightened for your specific setup. That’s true whether you’re talking about a £40 home router or an enterprise-grade appliance costing thousands.
Two Types of Firewall: Boundary and Host-Based
The UK’s Cyber Essentials scheme, run by IASME on behalf of the NCSC, splits firewalls into two categories, and most businesses need both.
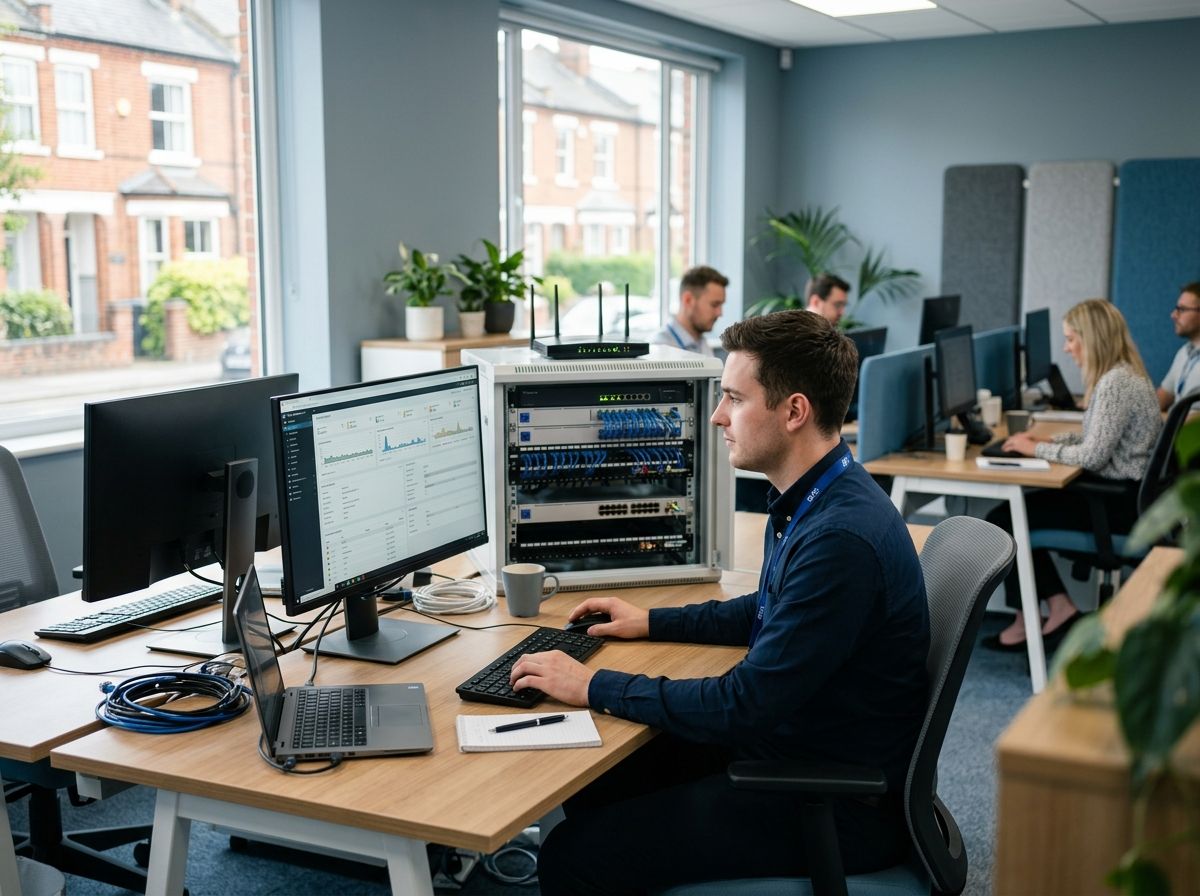
Boundary firewalls sit at the edge of your network, between everything you control and the wider internet. This is usually your office router or a dedicated firewall appliance, and its job is to filter traffic before it ever reaches an internal device.
Host-based (software) firewalls run on individual devices, laptops, desktops, and servers, and protect that single machine wherever it connects. Windows comes with Windows Defender Firewall built in, and macOS has its own equivalent, both switched on by default in most cases.
If your team ever works from a coffee shop, home Wi-Fi, or anywhere outside your office network, the boundary firewall can’t help them, since they’re not behind it. That’s exactly why host-based firewalls matter just as much as the one on your router.
Firewall Configuration and Cyber Essentials
Firewalls are the first of five technical controls in Cyber Essentials, alongside secure configuration, security update management, user access control, and malware protection. If you’re pursuing certification, or simply want a sensible baseline, the scheme’s requirements are a useful checklist even if you never apply:
- A firewall must be enabled at the boundary of every internal network, and on every device that connects to untrusted networks
- Default administrator passwords on routers and firewalls must be changed to strong, unique ones before the device goes live
- Administrative interfaces should not be reachable from the internet, so no exposing your router’s login page to the public web
- Firewall rules should follow a “deny by default” approach, only opening the specific ports and services your business genuinely needs
- Any rule that’s no longer needed should be removed rather than left in place “just in case”
Cyber Essentials certificates last 12 months, so this isn’t a one-off task even if you do go for formal certification. It’s a routine you repeat.
How to Configure a Boundary Firewall (Router or Appliance)
- Log in and change the defaults. Most routers ship with a default admin password, often printed on the device itself. Change it immediately to something unique, and change the default network name (SSID) too if it identifies the make or model.
- Update the firmware. Check for the latest firmware version before doing anything else, since older versions can carry known vulnerabilities.
- Disable remote management unless you specifically need it, and if you do, restrict it to particular IP addresses rather than leaving it open to the whole internet.
- Set the default policy to deny. Block all inbound connections by default, then add specific allow rules only for the services you actually run, such as a VPN or a hosted web server.
- Segment your network where you can. Guest Wi-Fi, staff devices, and anything like point-of-sale or payment systems should sit on separate networks (VLANs) so a problem on one doesn’t spread to the others.
- Turn on logging so you have a record of what’s being blocked and allowed, which is invaluable if something goes wrong later.
- Document every rule you create, including why it exists and who asked for it. A rule with no record behind it is very easy to leave in place long after it’s needed.
How to Configure a Software Firewall (Windows and macOS)
For most staff laptops, the built-in firewall is enough, provided it’s switched on and set correctly.
On Windows: open Windows Security, go to Firewall & network protection, and confirm it’s turned on for each network profile (Domain, Private, and Public). Review the list of allowed apps regularly and remove anything you no longer recognise or use.
On macOS: open System Settings, go to Network, then Firewall, and switch it on. Under Options, you can block all incoming connections except those essential for basic services, which is a sensible default for most laptops that travel outside the office.
Either way, don’t rely on the factory defaults alone. A firewall that’s switched on but never reviewed will still let through anything an installed app requests, which over time adds up to a fairly wide-open door.
Common Firewall Misconfigurations to Avoid
Misconfigured firewalls have caused some genuinely large breaches. A 2019 incident at Capital One, caused by a misconfigured web application firewall, exposed the personal data of more than 100 million customers, one of the clearest public examples of how a single overlooked setting can cause enormous damage.
Common mistakes worth checking for on your own setup:
- Leaving the default “allow all” rule active instead of switching to deny by default
- Management interfaces still reachable from the public internet
- Overly broad outbound rules that let any device talk to anywhere, rather than only what it needs
- Rules left in place for services or staff that no longer exist
- No logging, so nobody notices unusual traffic until something’s already gone wrong
How Often Should You Review Firewall Rules?
Set a recurring review, ideally every three to six months, and always after any change to your network, such as a new supplier connection, a new remote worker, or a new piece of software that needs a specific port opened. Cyber Essentials assessors will expect to see evidence that reviews actually happen, not just that a firewall exists.
FAQs
What is firewall configuration?
Firewall configuration is the process of setting the rules that decide which network traffic a firewall allows through and which it blocks, based on things like IP address, port, and protocol. A well-configured firewall follows a deny by default approach, only permitting traffic you’ve specifically approved.
Do I need a firewall for Cyber Essentials?
Yes. Firewalls are one of the five mandatory technical controls in the UK’s Cyber Essentials scheme, covering both boundary firewalls on your network and host-based firewalls on individual devices.
What’s the difference between a boundary firewall and a software firewall?
A boundary firewall protects your whole network at the point where it meets the internet, usually your router or a dedicated appliance. A software firewall runs on one device and protects it wherever it connects, which matters for laptops used outside the office.
Is Windows Defender Firewall good enough for a small business?
For most small businesses, yes, provided it’s switched on for every network profile and the list of allowed apps is reviewed regularly. Larger or higher-risk businesses may still want a dedicated boundary firewall appliance alongside it.
How often should firewall rules be reviewed?
Every three to six months is a sensible baseline, and always after a network change such as a new remote worker, supplier connection, or newly installed software that needs a specific port.
Can a misconfigured firewall cause a data breach?
Yes, and it has. The 2019 Capital One breach, which exposed data belonging to more than 100 million people, was traced back to a misconfigured web application firewall.
Should remote management be enabled on my router?
Only if you genuinely need it, and if you do, restrict access to specific IP addresses rather than leaving it open to any device on the internet. For most small businesses, remote management should stay switched off.
Does a firewall protect against all cyber attacks?
No single control does, but the NCSC estimates that its five basic technical controls, firewalls included, would prevent around 80% of the common attacks UK organisations face. A firewall is a foundation, not a complete solution on its own.